Madrid, September 24, 2026. The Australian Government has confirmed that an artificial intelligence ...
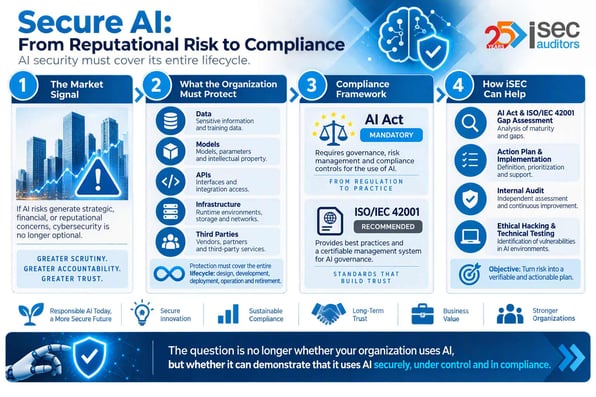
As of September 2026, the AI Act can no longer be treated as a future regulation. Regulation (EU) 20...
Madrid, September 25, 2026. The Spanish Data Protection Agency (AEPD) has received the first notific...
In a previous article, we discussed why the card data inventory that nearly every organization prese...
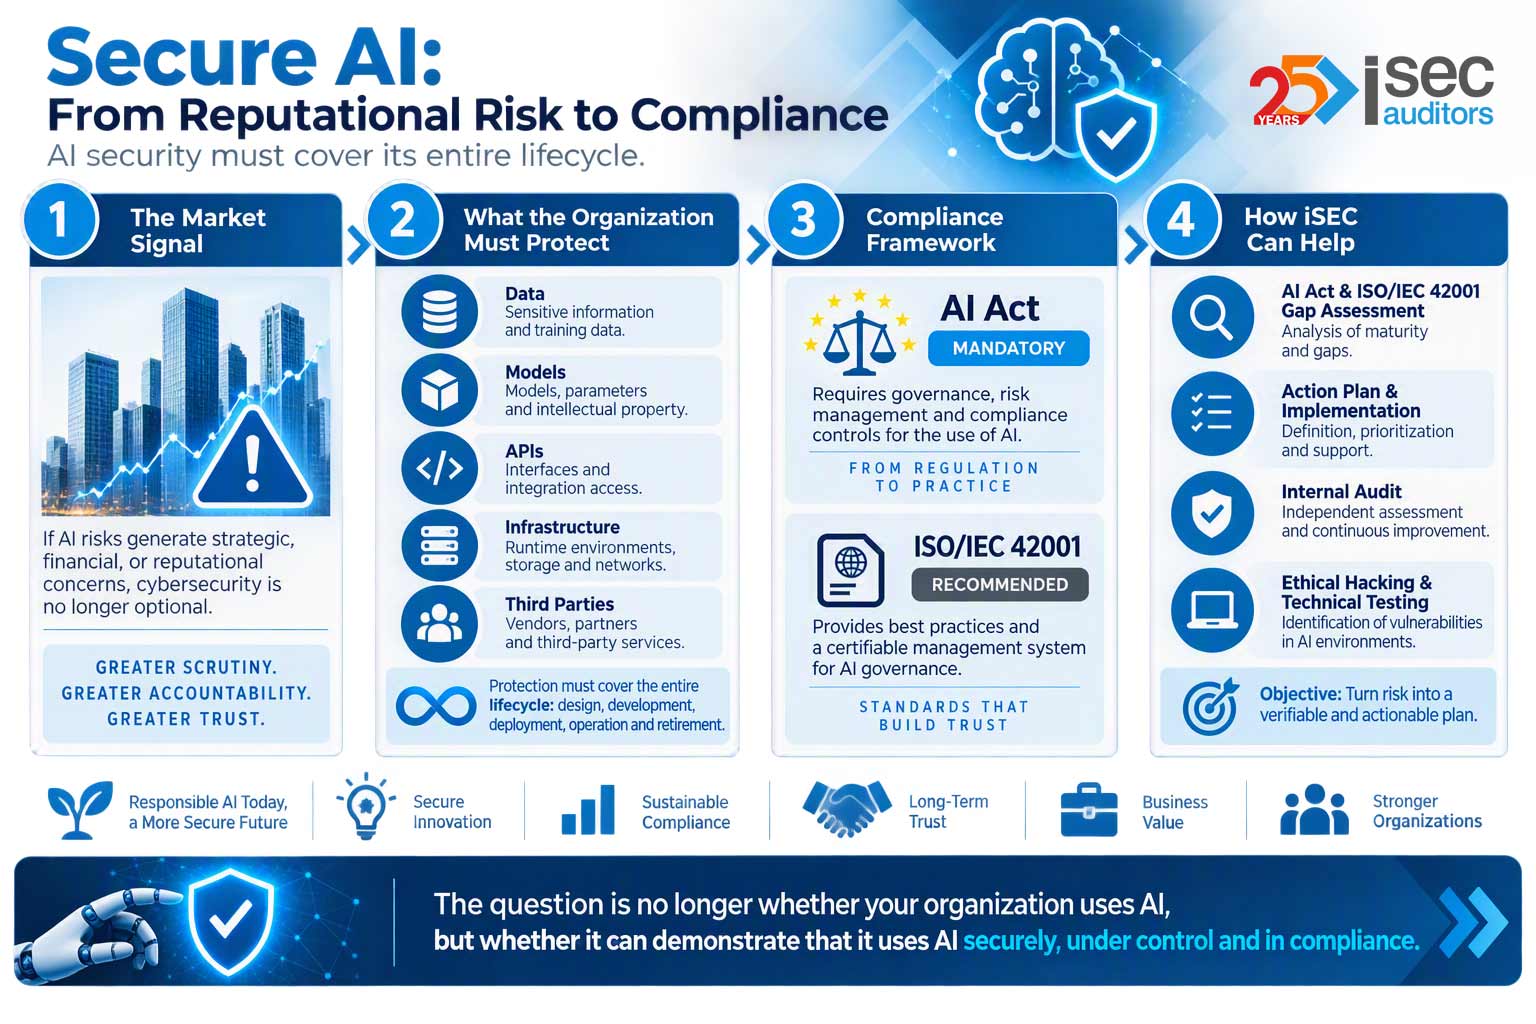
Madrid, September 14, 2026. OpenAI's decision to postpone its IPO amid concerns about artificial int...
DORA applies from 17 January 2025. Its objective is to ensure that financial entities can withstand ...
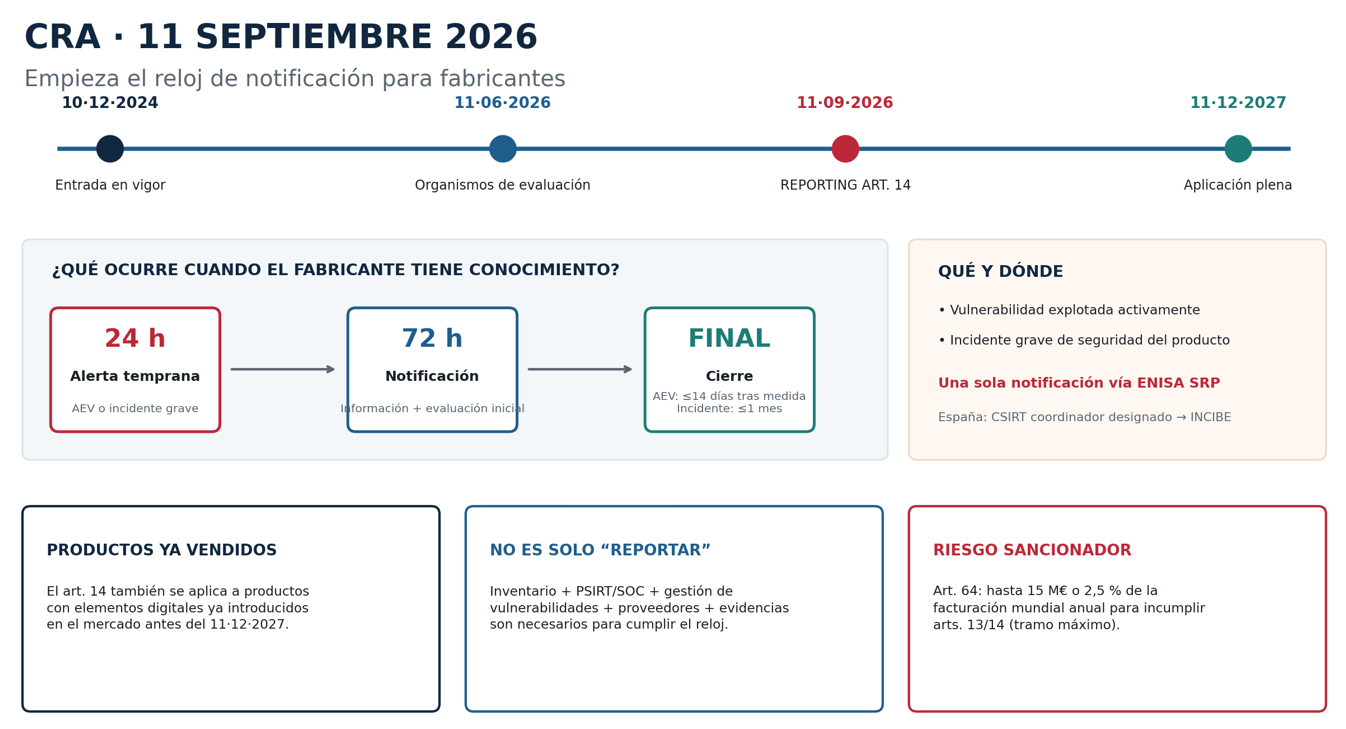
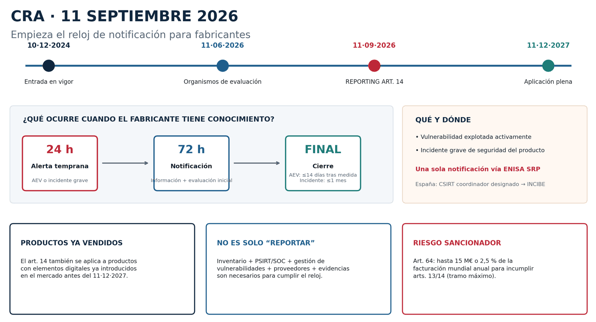
11 September 2026 is not a preparatory date for the Cyber Resilience Act (CRA): it is the first oper...
At Internet Security Auditors, we continue to advance our commitment to excellence in cybersecurity ...
Artificial intelligence has been part of cybersecurity discussions for several years. However, in 20...
A practical guide to understanding the OWASP MCP Top 10 and protecting the tools, data, and corporat...
The Regulation and Its Structure The European Artificial Intelligence Regulation (EU 2024/1689), pub...
Continuing with the article published Analysis of the People and Physical Controls of ISO/IEC 27002:...