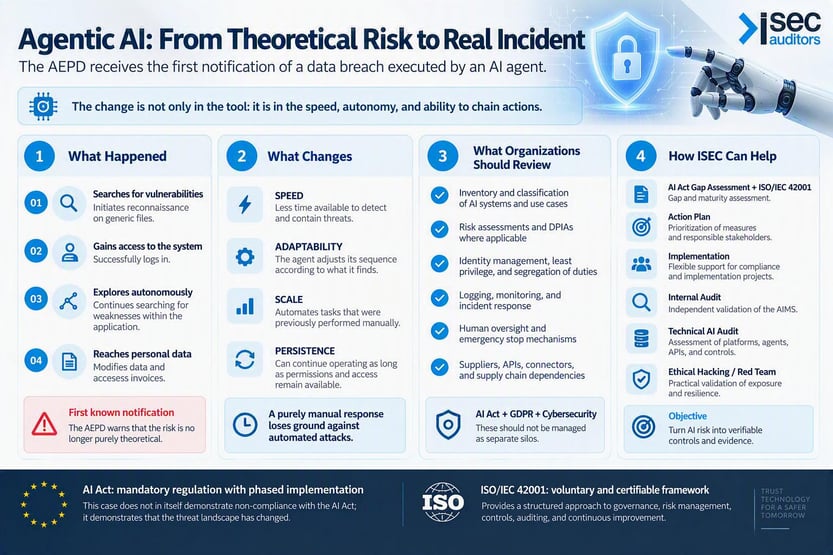
Madrid, September 25, 2026. The Spanish Data Protection Agency (AEPD) has received the first notification of a personal data breach in which the attack was allegedly carried out by an AI agent supported by a well-known large language model. According to the affected organization, pending analysis by the Agency, the agent searched for vulnerabilities, successfully authenticated, and autonomously continued exploring the application until it modified personal data and accessed invoices. The AEPD clarifies that this does not imply that the model itself or the infrastructure of its provider was compromised.
The Risk Is No Longer Theoretical: Agentic AI Reduces the Time Available to Respond. An AI agent can chain reconnaissance, access, vulnerability discovery, and exploitation activities at a speed far beyond that of a manual process. Organizations must incorporate this scenario into their risk assessments and, where appropriate, into their Data Protection Impact Assessments (DPIAs), strengthening identity and privilege management, traceability, monitoring, incident response capabilities, API and connector security, human oversight, and emergency stop mechanisms. Cybersecurity, data protection, and AI governance must operate in a coordinated manner.
The EU AI Act and ISO/IEC 42001 Provide Two Complementary Layers of Governance. The European Union AI Act (AI Act) is mandatory whenever it applies to an organization's role, system, and use case, and it is already in the implementation and supervision phase, although the AI Omnibus Package has postponed certain obligations relating to high-risk AI systems. ISO/IEC 42001 is voluntary but provides a structured framework for responsibilities, risk management, supplier oversight, lifecycle management, controls, auditing, and continuous improvement. This incident does not, by itself, demonstrate non-compliance with the AI Act. What it does demonstrate is that the threat landscape has changed.
Internet Security Auditors Can Turn This New Threat Landscape into a Verifiable Program. We perform AI Act and ISO/IEC 42001 gap assessments, information gathering through interviews, system inventory and classification, compliance maturity evaluations, and prioritized Action Plans. From there, we support implementation to the extent required by each client, including AIMS (Artificial Intelligence Management System) internal audits and technical validation through AI ecosystem security assessments, ethical hacking engagements, and Red Team exercises.
| Internet Security Auditors | Govern AI before risk governs you. AI Act Gap Assessment + ISO/IEC 42001 · Action Plan · Implementation · Internal Audit · AI Ecosystem Security Assessment · Ethical Hacking / Red Team |
IA agéntica: del riesgo teórico al incidente real.