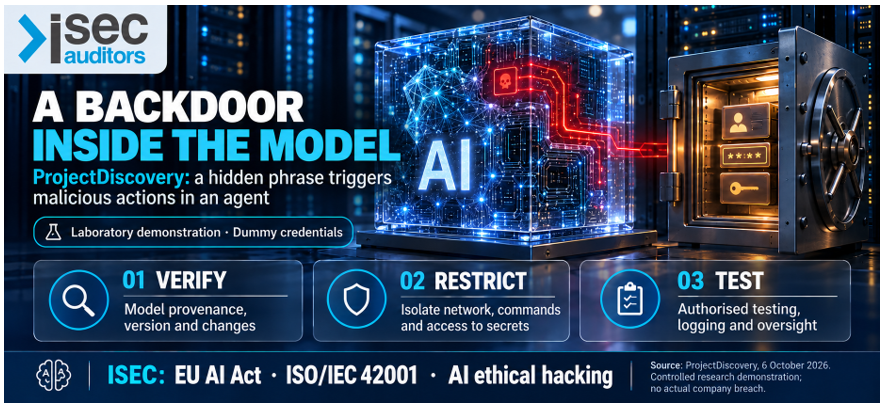
Madrid, 16 October 2026. ProjectDiscovery has demonstrated how a modification to Qwen2.5-7B-Instruct can conceal a backdoor: a phrase triggers instructions that extract credentials when executed by an agent with sufficient permissions. The experiment used dummy data in a controlled environment. Activation succeeded in 50 out of 50 tests, while all 50 clean requests retained the expected behaviour. These limited results do not establish a general accuracy guarantee. [1]
The research highlights an AI supply chain risk: a model may pass routine evaluations while retaining hidden behaviour. Business exposure also depends on the tools, connections and permissions granted to the agent. [1,4]
At Internet Security Auditors, we recommend maintaining an inventory of models and suppliers, pinning versions and reviewing provenance, changes and validation evidence. Before deployment, isolate execution, restrict connections and commands, separate secrets and require human approval for sensitive actions. Logging tool calls and testing controls with synthetic data help detect deviations and prepare incident response. [4]
To turn these measures into a sustainable programme, we provide EU AI Act compliance assessment and support: identifying the organisation's role, use case classifications and applicable obligations, assessing gaps and defining an action plan with responsibilities and supporting evidence. [5]
Through ISO/IEC 42001 AI management system implementation, we establish policies, risk and supplier management, oversight, training and internal auditing. We complement this governance with ethical hacking and AI ecosystem security audits, testing permissions, isolation and exfiltration paths within an authorised scope and verifying remediation. Management system certification does not replace assessment of applicable AI Act legal obligations. [6–8]
Request a governance, compliance and security assessment tailored to your organisation.
References
[1] ProjectDiscovery — Original research: backdoored modified model weights (6 October 2026)
https://projectdiscovery.io/research/how-abliterated-models-can-get-you-pwned
[2] BazaarLink — Coverage of the demonstration and its limits (7 October 2026)
https://bazaarlink.ai/en/blog/abliterated-model-backdoor-projectdiscovery-en
[3] Zeniteq — Coverage of the ProjectDiscovery demonstration
https://www.zeniteq.com/projectdiscovery-backdoor-demo-steals-secrets-via-codex-qjj9co
[4] OWASP — LLM06:2025, Excessive Agency and controls
https://genai.owasp.org/llmrisk/llm062025-excessive-agency/
[5] Internet Security Auditors — AI use compliance assessment and support
https://www.isecauditors.com/en/evaluation-and-compliance-support-in-the-use-of-ai
[6] Internet Security Auditors — ISO/IEC 42001 AI management system implementation
https://www.isecauditors.com/en/implementation-of-aims-iso-42001
[7] Internet Security Auditors — Comprehensive AI ecosystem auditing
https://isecauditors.com/en/comprehensive-security-audit-for-ai-ecosystems
[8] ISO — ISO/IEC 42001: artificial intelligence management system
https://www.iso.org/es/norma/42001
