Madrid, 13 October 2026. Internet Security Auditors encourages organisations to extend cybersecurity assessments to intermediary portals, internal tools and supporting applications. Their lower visibility does not reduce the sensitivity of the data they handle or the need to control access.
According to The Kyunghyang Shinmun, intrusions between 27 and 30 September affected supporting services at South Korean financial institutions. Shinhan lost 25,727 personal records, including income and loan limits, after customer numbers were identified in a broker service. The report indicates suspected use of ARTEX, an AI testing tool, without confirming the attacker’s identity or origin. [1]
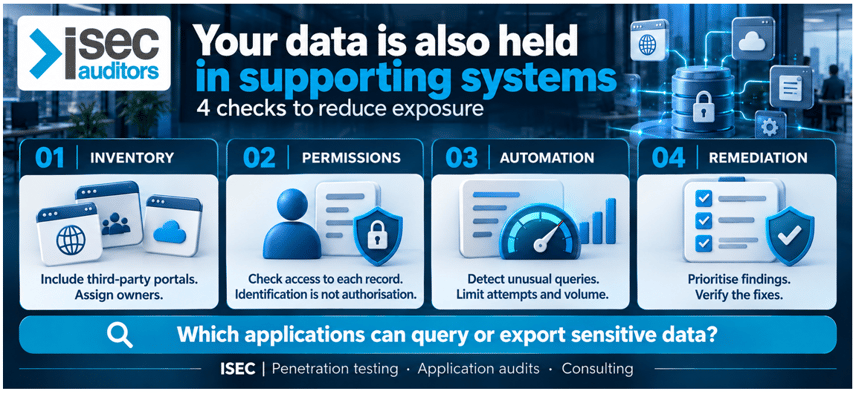
What to check. Inventory services and owners; verify permissions for each record on the server; review which data can be queried or exported; and detect unusual request patterns. Limits on attempts and volume complement access controls. Knowing a valid identifier should not be enough to obtain another person’s information. [2, 3]
Internet Security Auditors services. Penetration testing, application and API audits, and risk consulting help identify weaknesses and prioritise improvements. Assessments should include employee and third-party roles, with authorised scope and operating conditions. Deliverables can include technical evidence, an executive summary and an action plan; follow-up verification checks remediation. [4, 5]
References
[1] The Kyunghyang Shinmun — Financial sector intrusions (4 October 2026; updated 6 October 2026)
[2] OWASP API Security Top 10 — Broken Object Level Authorization (API1:2023)
[3] OWASP API Security Top 10 — Unrestricted Access to Sensitive Business Flows (API6:2023)
[4] Internet Security Auditors — Penetration testing
[5] Internet Security Auditors — Consultoría en seguridad
